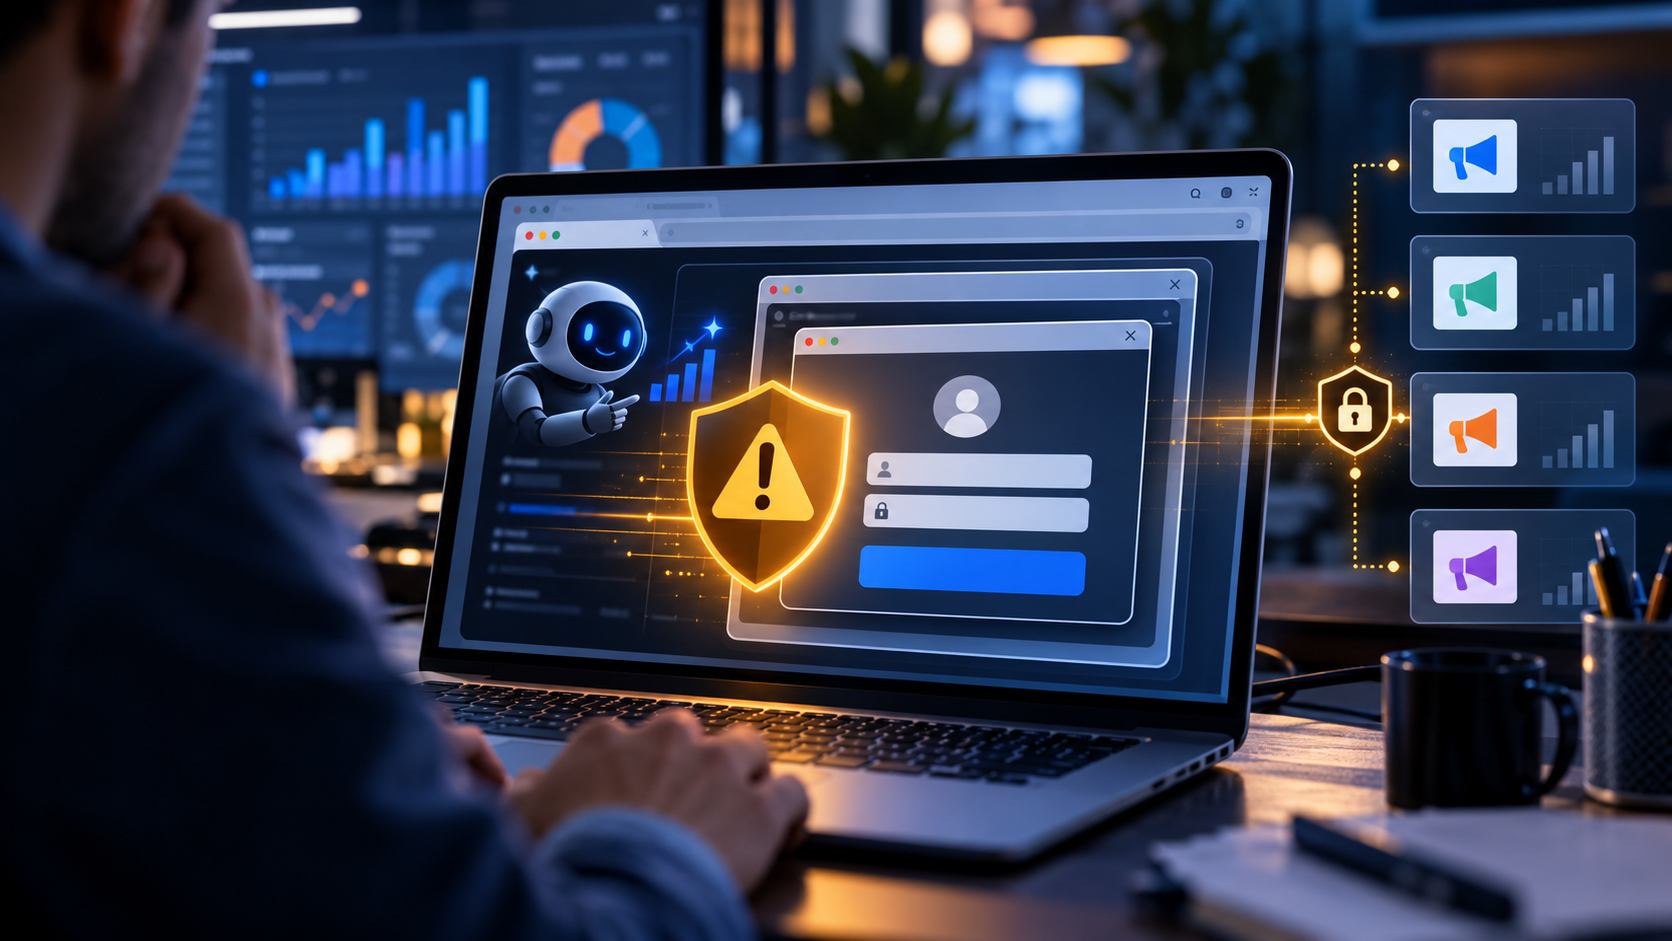
Original editorial illustration; it is not a capture of an active phishing page and does not reproduce a real brand interface.
Security company Island has documented an advertising-led phishing operation that imitates popular artificial-intelligence products and marketing tools. Its 6 October 2026 investigation describes fake experiences styled after products associated with ChatGPT, Gemini, Claude, Perplexity, Manus and an invented tool called Muse Ads. The campaign uses a browser-in-the-browser technique to display a convincing sign-in window inside a malicious page, gathers device and session details, and can route the victim through a human-operated state machine. Island says it observed hundreds of victim submissions and that the activity remained ongoing when it published.
Independent technology reports, including TechRadar's coverage and The Hacker News summary, help corroborate the campaign description, but Island remains the primary source for telemetry and victim-count language. The number is not a global prevalence estimate. It describes what one research team observed in its visibility, and the attackers may change domains, creative and lures.
Why marketing teams are attractive targets
Marketers routinely connect advertising accounts, analytics, social pages, cloud files and creative tools. They work quickly across many vendors and are conditioned to authorize integrations. An advertisement promising an AI campaign generator or a new optimization product can therefore look like ordinary professional discovery. The perceived reward is immediate: faster creative, lower media cost or a competitive advantage.
A compromised marketer may expose more than a personal inbox. Advertising accounts can contain payment methods, customer audiences, pixels, catalogs and administrator privileges. Email access can reset other services. A stolen session or multi-factor code may allow an attacker to act before the victim understands what happened. Agencies are especially exposed because one employee can have access to multiple client businesses.
How the browser-in-the-browser illusion works
In a legitimate OAuth flow, the identity provider opens a real browser window or navigates to its genuine domain. The address bar and browser controls belong to the browser. In a browser-in-the-browser attack, the malicious page draws a window-shaped element that imitates those controls. It can display the correct logo and a believable address while the entire object remains part of the attacker's page.
The visual difference can be hard to notice, especially on a small screen or when the person expects a connection step. A user may enter credentials, approve a prompt or provide a one-time code. The fake interface can react in real time. That is why advice limited to checking the logo or spelling is insufficient; the attacker can copy visual assets accurately.
Human operation makes the flow adaptive
Island's description of a state machine and human involvement matters. A static phishing kit gives every victim the same path. An operator-assisted flow can wait for the right moment, request a second factor, display an error, or redirect the person to a real site after capture. That variability defeats training that expects one suspicious sequence.
Device fingerprinting can help the attacker decide whether the visitor appears to be a researcher, automated scanner or target. The campaign can show harmless content to some visitors and the credential lure to others. This conditional delivery makes detection and reproduction harder. Security teams should collect network, endpoint and identity evidence together rather than relying on a screenshot alone.
The fake product is part of the persuasion
The lure does not always impersonate an established product exactly. Attackers can invent a plausible tool, run polished advertisements and borrow the language of AI productivity. Island notes that a fake skin appeared within eight days of the Muse launch. Speed matters because buyers have little prior knowledge of a new product's authentic interface or domain. Curiosity fills the trust gap.
This is a brand and media-governance issue as well as an IT problem. Paid distribution can make a fraudulent product look validated. Landing-page polish and familiar identity prompts create social proof. Procurement teams need a method for verifying a vendor before any employee connects an account, even when the discovery source is a reputable advertising platform.
Establish a vendor-verification gate
Require employees to find the vendor independently through an approved directory, known official domain or verified corporate documentation. Do not authorize an integration from the advertisement's landing page. Confirm the legal entity, privacy documentation, support channel, requested permissions and domain history. For a new vendor, ask security to review the OAuth application identifier and scopes.
Create an allowlist for high-risk connections such as advertising administrators, customer-data platforms and email. A request outside the list triggers review. This does not mean banning experimentation; provide a sandbox account with no production audience, payment method or client data. A secure path must be faster than bypassing the policy, or teams will create shadow workflows.
Prefer origin-bound authentication
Island recommends phishing-resistant approaches such as passkeys or hardware-backed credentials. These methods can bind authentication to the genuine origin, so a credential intended for one domain cannot simply be replayed on a visually similar page. Adoption should focus first on email, identity administration, advertising business managers and cloud storage because compromise there creates broad downstream access.
Multi-factor authentication remains valuable, but one-time codes can be phished in real time. Push fatigue can also induce approval. Configure number matching and risk controls where available, remove weak recovery routes, and maintain emergency access accounts securely. Authentication strength must be combined with least privilege and session monitoring; no single control eliminates every path.
Minimize privileges and separate client environments
Review who has administrator access to each platform. Most campaign work does not require ownership-level rights. Give employees the minimum role for the task, set time limits for contractors and remove dormant accounts. Use separate named identities rather than shared logins. For agencies, isolate clients so a compromise in one workspace does not automatically cross into another.
Maintain an access register that records platform, owner, administrators, recovery contacts, authentication method and last review. Reconcile it monthly against staff changes. Protect API keys and automation tokens in an approved secrets manager. A phishing event often reveals old access that nobody remembered; disciplined inventory reduces the blast radius.
Train with the actual decision, not a generic warning
Traditional awareness training often says do not click suspicious links, while a marketer's job requires opening links and evaluating tools. Train the safer decision: pause before connecting an account; navigate independently to the vendor; inspect the real browser origin; verify the requested scope; and use the sandbox. Demonstrate how a drawn window differs from an actual browser window without teaching evasion techniques.
Run a tabletop exercise around a fake AI-ad product. Include marketing, security, procurement, legal and client service. Ask who pauses campaigns, revokes tokens, informs clients, preserves evidence and handles fraudulent spend. Measure reporting time and completeness, not only whether someone clicked. Early reporting can turn a mistake into a contained incident.
A 30-day control test for agencies
In week one, inventory privileged identities, current OAuth applications and recovery methods. In week two, enforce stronger authentication for the highest-risk systems and remove unnecessary administrators. In week three, test the vendor-review and sandbox path with a real low-risk tool. In week four, run a simulated incident and verify revocation, log access and communication.
Set measurable acceptance criteria: all business-manager owners identified; no shared administrator password; 100 percent of priority identities using the strongest supported phishing-resistant method; unauthorized OAuth grants reviewed within one business day; and simulated reports reaching security within a defined target. Record exceptions and owners. Percentages describe internal goals, not claims that the controls make compromise impossible.
Incident response when someone connects
Treat a reported connection as urgent without blaming the employee. From a trusted device, revoke active sessions and OAuth grants, reset affected credentials, verify multi-factor and recovery settings, and inspect email forwarding and account administrators. Contact advertising-platform support through official channels. Preserve the malicious URL, advertisement identifier, time and screenshots if safe.
Review campaign changes, billing, audience exports and new users across connected clients. Notify affected organizations according to contracts and applicable law. If personal data may be involved, engage privacy and legal teams immediately. Do not ask the victim to revisit the site for evidence. Update detection and the vendor blocklist, then communicate a concise lesson to the broader team.
GCC and healthcare implications
Saudi and UAE agencies often manage bilingual campaigns, messaging accounts and high-value client portfolios through a small operations team. Fast adoption of AI tools can amplify both productivity and access risk. Procurement and security guidance should be available in Arabic and English, with an escalation route usable outside standard hours. Local data-protection and contractual duties may affect notification and investigation.
Healthcare marketing adds sensitive context. Even if an advertising platform should not contain clinical records, audiences, inquiries and lead forms may reveal health interests. Never use a marketing integration as a shortcut around approved health-data systems. Separate patient communication from ad-platform experimentation, minimize exported fields and involve privacy leadership before connecting a new AI vendor.
Limits of the current evidence
Island's report is a point-in-time investigation from a security vendor with particular visibility. Hundreds of observed submissions do not reveal the global number of victims or success rate. The names, domains and interface can change. Secondary reporting may repeat the same primary claims, so several articles are not necessarily independent confirmation.
Defenders should use indicators from the report but focus on durable controls: verified navigation, origin-bound authentication, least privilege, application review and fast response. A blocklist alone ages quickly. Avoid publicly sharing operational details that help attackers test defenses. Update the threat model as new evidence appears.
Karim's strategic decision
Karim can add a marketing-access security review to growth and AI-operations engagements. It would map advertising and creative privileges, review how teams discover vendors, establish a sandbox and approval path, and run a bilingual incident exercise. The service should be delivered with qualified security and legal partners where technical investigation or regulatory interpretation is required.
The commercial decision is simple: do not scale AI-tool adoption until the access layer is visible and recoverable. Success is fewer unnecessary administrators, stronger authentication coverage, faster reporting and a tested revocation process, not a promise of zero incidents. The campaign shows that attackers understand marketing workflows. Growth operations must therefore treat identity security as part of campaign performance and client trust.
Comments
No published comments yet.